Premium article
The guidance reflects the agencies’ supervisory oversight and their examinations of financial institutions’ third-party risk management practices.
The guidance reflects the agencies’ supervisory oversight and their examinations of financial institutions’ third-party risk management practices.

The guidance explains how covered firms can conduct risk assessments that evaluate, identify, analyze and prioritize cybersecurity risks.

Document answers two new FAQs and updates another, addressing CIPs and use of government-issued verifiable digital credentials.
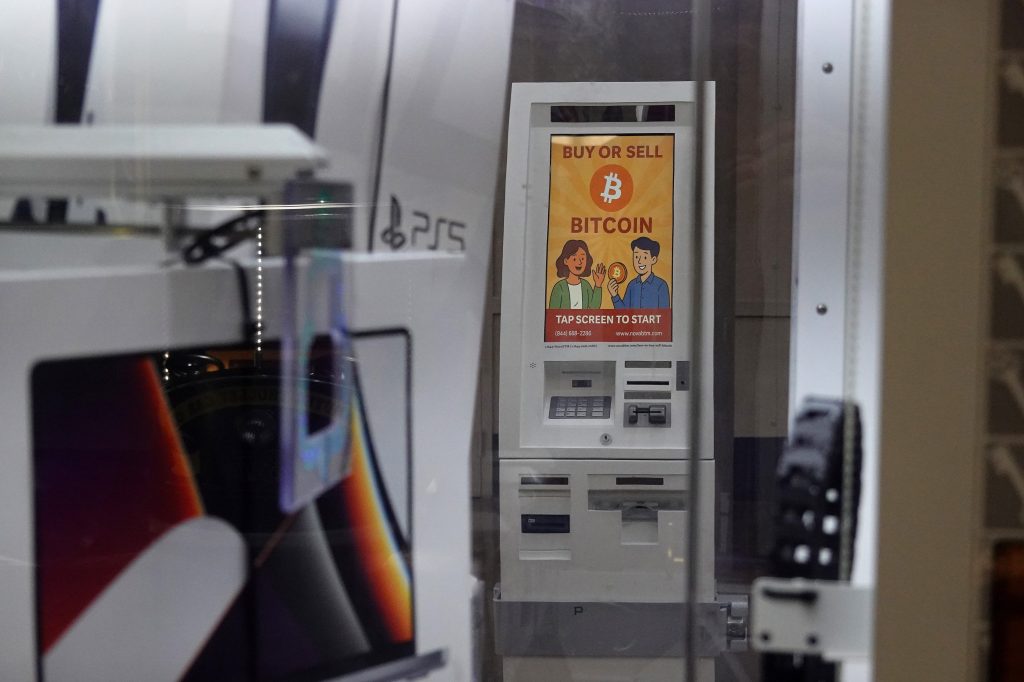
The growing number of such scams, FinCEN said, are largely perpetrated by transnational criminal organizations operating “industrial-scale scam compounds” with networks of criminal actors.
Kadas spoke of AI’s ability to identify more relevant communications, and further investigations that someone at the bank would need to perform.
SEC wants to scrap 2010 restriction that blocks advisers who made recent political contributions from working with state and local pension plans.
The main message: Banks need to take certain precautions when discussing information that could reveal the existence of a SAR.
The agencies signed a MOU to support the sharing of nonpublic information about regulated products and possible violations of law.