Skip to Primary Navigation

Dior’s Shanghai branch penalized for non-compliant cross-border data transfer
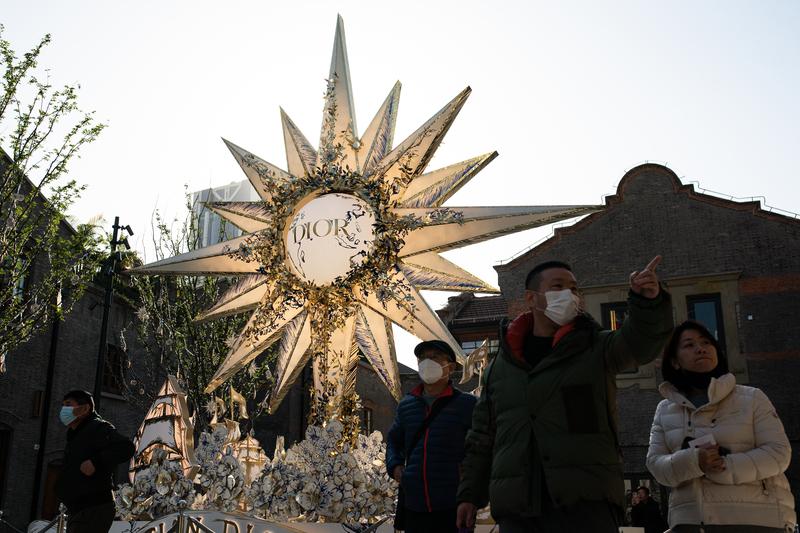
Pedestrians walks past a huge Christian Dior installation at a shopping mall on December 14, 2022 in Shanghai, China.
Dior installation at a Shanghai mall. Photo: Yifan Ding/Getty Images

Investigation into Dior’s global data breach uncovered compliance shortcomings in cross-border data transfer, user consent, and data security.

In May of this year, multinational corporation (MNC) Dior experienced a global customer data breach. On May 12, 2025, consumers worldwide, including those in China, received a text message from Dior informing them that on May 7, 2025, it was discovered that some consumer information had been accessed by unauthorized

Get full access, free for a month

Start your 28-day free trial to continue reading and access all content on GRIP – no payment details required.

What’s included:

  • Every new article, plus our 5,000+ archive
  • Daily regulatory insight and guidance
  • Exclusive interviews and in-depth analysis
  • Coverage of industry-leading events and conferences
  • All podcasts and videos, featuring industry experts
  • The full set of Rules Navigator tools
  • An ad-free experience