The incident offers a concrete scenario against which organizations can stress-test their existing programs: three steps to consider.
The incident offers a concrete scenario against which organizations can stress-test their existing programs: three steps to consider.
Rosemarie Connell is senior managing director at Integrated Solutions, following a career as a commodities trader.
A new supervisory review highlights incident learning and ICT risk management among key gaps in DORA compliance.
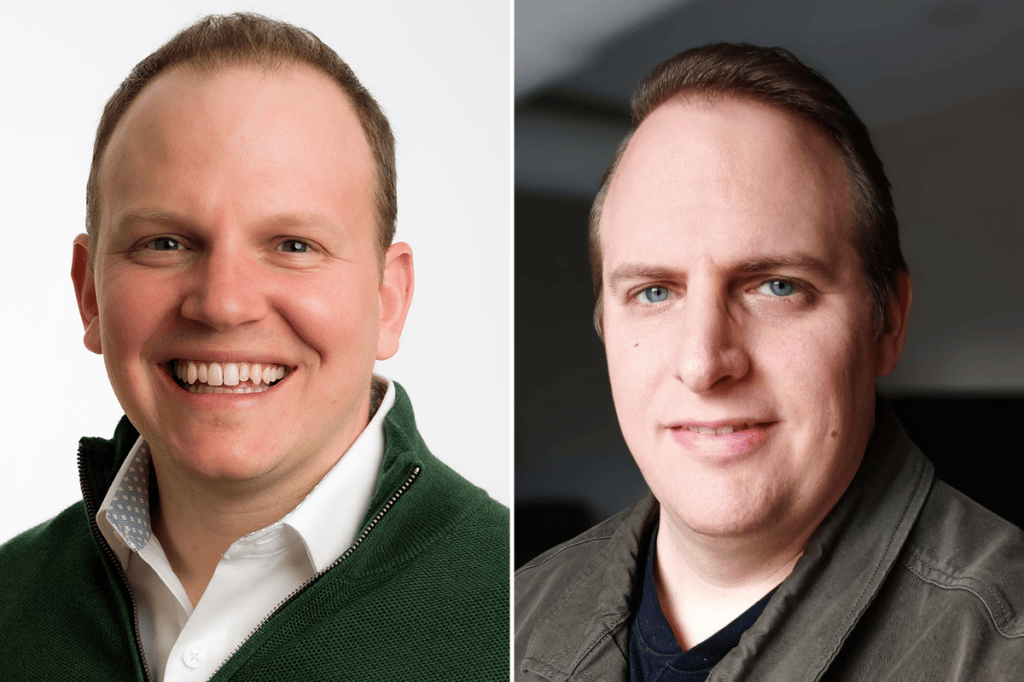
Martano and Kakolowski spoke about AI security investment, security program maturity, and the burdens of overseeing cyber risk, thanks to AI.
Speaking to GRIP, the ECA shares how organizations can make the most of its latest report’s findings.
CIRO said it delivered on its 2026 Annual Priorities and made significant progress on the objectives in its Strategic Plan.
We consider the emerging standards and the practical, legal, and governance steps organizations should take now.
The vulnerability was real; the exploit was impossible; the EU Cyber Resilience Act reporting obligation was … unclear? We discuss the intricacies of the Act and compare with UK approach.