Premium article
Speaking to GRIP, the ECA shares how organizations can make the most of its latest report’s findings.
Speaking to GRIP, the ECA shares how organizations can make the most of its latest report’s findings.
The vulnerability was real; the exploit was impossible; the EU Cyber Resilience Act reporting obligation was … unclear? We discuss the intricacies of the Act and compare with UK approach.
The Cyber Resilience Act (CRA) brings manufacturers of products with digital elements under strict deadlines and new compliance responsibilities.
The Action Plan does not create new legal obligations but sets out steps for operationalizing the AI Act, NIS2, DORA, and the Cyber Resilience Act.
Charles Herbert and James Clark discuss the potential for regulatory alignment across two areas of importance – digital law, and financial services regulation.
Regulation to push European businesses and third-country suppliers to consider potential exposure to government influence when assessing their technology vendor relationships.
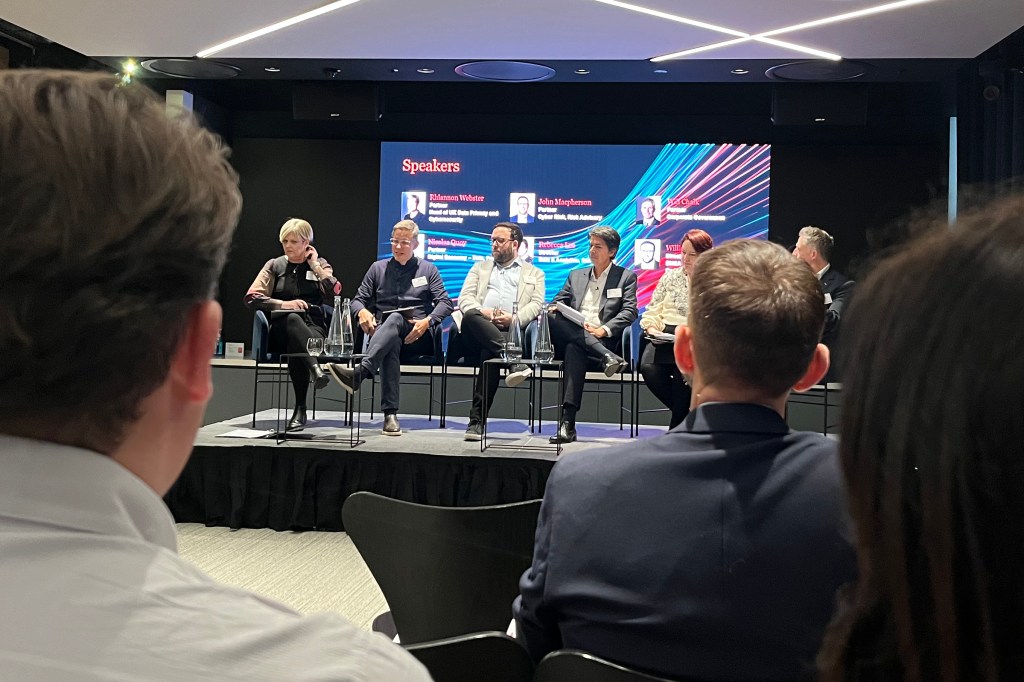
An Ashurst panel, together with guest speaker Will Barlow of Crowdstrike, discussed what steps you should be taking to prepare for a cybersecurity incident.
The EU CRA makes cybersecurity mandatory for all products with digital elements.