Skip to Primary Navigation

US security bodies highlight 10 most common cybersecurity misconfigurations

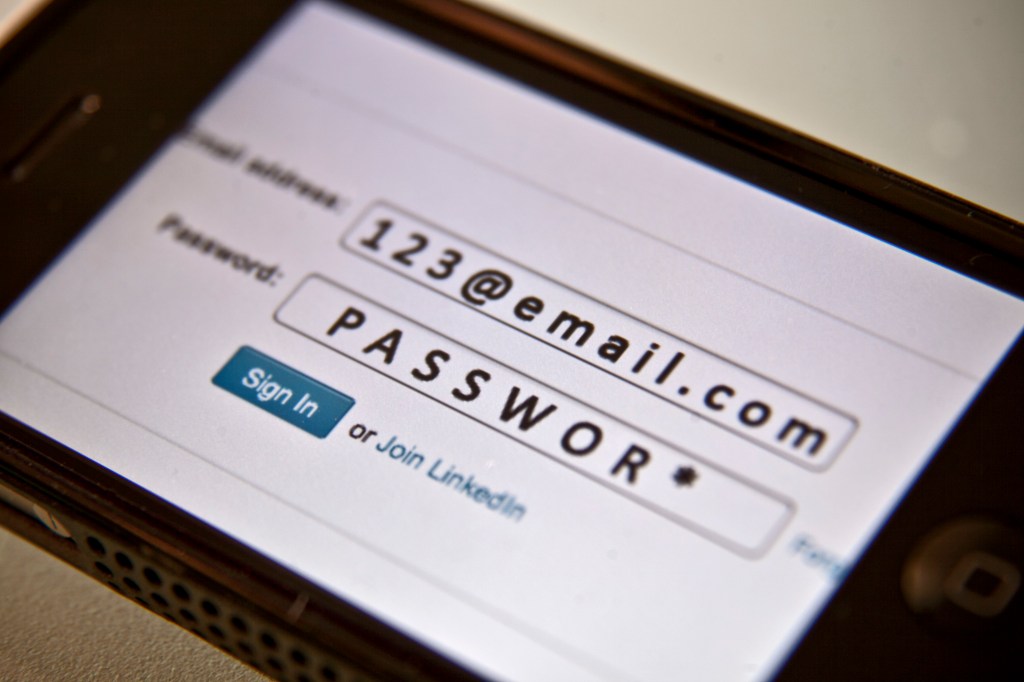
Poor password selection shown on screen
Photo: Ted Soqui/Corbis via Getty Images

NSA and ISA say findings indicate ‘systemic weakness’ in many large organizations.

Retaining default configurations of software and applications is the most common of 10 security risks highlighted by the US National Security Agency (NSA) and Infrastructure Security Agency (ISA).

The two agencies have issued a joint cybersecurity advisory (CSA) in which the 10 most common network misconfigurations are listed. That list is:

  1. Default

Get full access, free for a month

Start your 28-day free trial to continue reading and accessall content on GRIP – no payment details required.

What’s included:

  • Every new article, plus our 5,000+ archive
  • Daily regulatory insight and guidance
  • Exclusive interviews and in-depth analysis
  • Coverage of industry-leading events and conferences
  • All podcasts and videos, featuring industry experts
  • The full set of Rules Navigator tools
  • An ad-free experience