Skip to Primary Navigation

Lessons from Spain's first reported agentic AI data breach

The incident offers a concrete scenario against which organizations can stress-test their existing programs: three steps to consider.
Edward Machin, Ropes & Gray

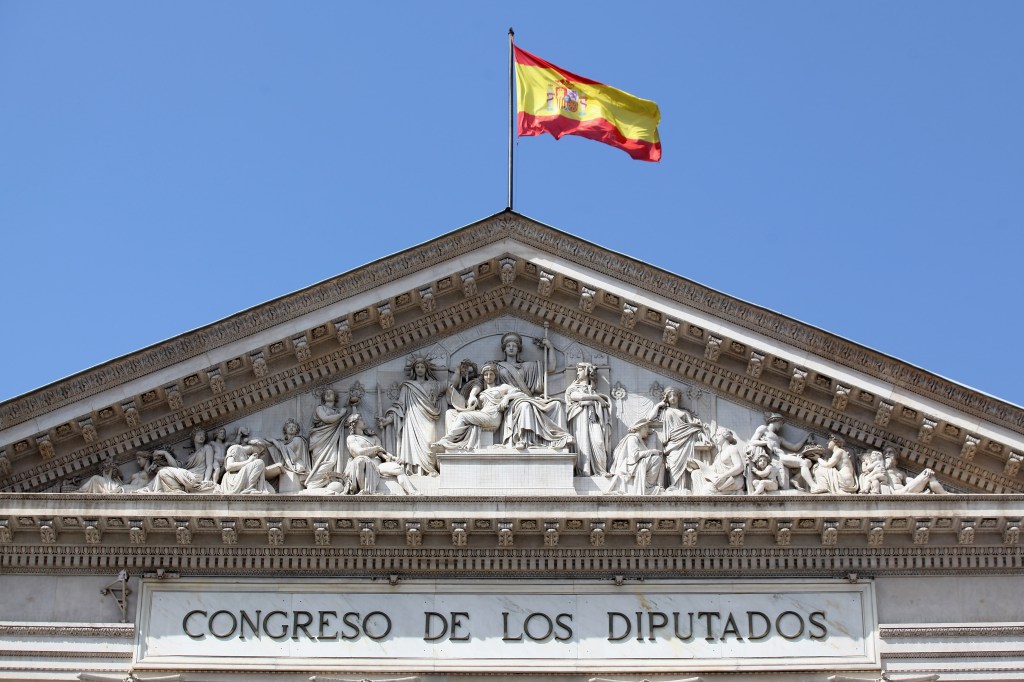
Last month, the Spanish data protection regulator (AEPD) disclosed that it had received the first notification of a personal data breach in which the incident had reportedly been executed using an AI agent that used a known large language model (LLM). The incident raises a question that organizations across Europe will increasingly

Get full access, free for a month

Start your 28-day free trial to continue reading and access all content on GRIP – no payment details required.

What’s included:

  • Every new article, plus our 6,000+ archive
  • Daily regulatory insight and guidance
  • Exclusive interviews and in-depth analysis
  • Coverage of industry-leading events and conferences
  • All podcasts and videos, featuring industry experts
  • The full set of Rules Navigator tools
  • An ad-free experience