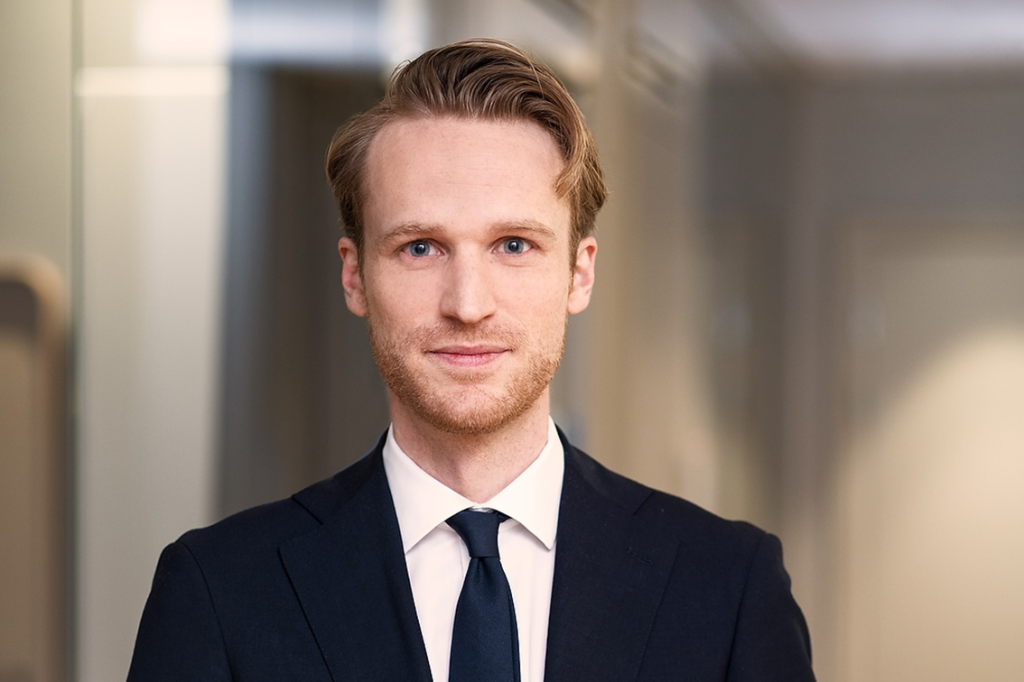
Fredrik Gustafsson is partner in TM & Partners’ Tech group, where he specializes in data protection, tech regulation, and IT contracts. Fredrik’s client engagements span start-ups, scale-ups, and established enterprises.
TM & Partners is a leading Swedish business law firm with a focus on transactions, combining deep expertise in data protection, technology law, and financial regulation.
What originally sparked your interest in data protection?
Fredrik Gustafsson: “Interestingly, data protection was not love at first sight.
When I joined my first law firm (in the pre-GDPR era), my team was tasked with handling a large volume of engagements related to data protection. At the time, I was asked to assist clients on various data protection matters and did well enough to be entrusted with more responsibilities.
As the engagements kept coming, I started recognizing patterns and connections – that was when genuine curiosity kicked in. What has kept me engaged ever since is the interplay between law, technology, business, and risk appetite, which I find fascinating.”
What is the biggest change you have observed – was it technological, legal, market-driven, or in another field?
“In retrospect, we have seen rather significant changes across all three fields – starting with a (legal) paradigm shift from next-to voluntary compliance to mandatory accountability frameworks.
On the technological developments side, the evolution of cloud services, Big Data, and now AI have fundamentally transformed how personal data is collected, processed, and used.
Finally, from a market perspective, data protection has slowly become a competitive differentiator. Companies that take privacy seriously use it as a competitive advantage and trust-building measure – it signals to customers and partners that the organization can be trusted with their data. Thus, GDPR compliance has now evolved from a legal necessity to a brand value.”
2026 marks 10 years since GDPR entered into force, representing a fundamental shift in how organizations approach personal data management. What are the main changes brought by GDPR and the biggest lessons drawn from the last decade?
“The first and among the most notable changes is the cultural shift. With GDPR, data protection made its way to an operational and strategic matter discussed in boardrooms and management teams and the DPO role gained broader mandate and transformed into a business-critical function.
GDPR enforcement has also matured, albeit unevenly – we have seen a clear escalation from the early years characterized by uncertainty and a few sanctions to major fines targeting players such as Meta, Amazon, and Uber. In Sweden, the Swedish Authority for Privacy Protection (IMY) was also cautious for a while but has now stepped up through a series of national decisions, more recently targeting data processors.
“GDPR remains the ‘horizontal constitution’ for personal data protection – it is technology-neutral and always applies alongside sector-specific regulation.”
Fredrik Gustafsson
“We have also seen increased requirements for documentation and accountability. Supervisors increasingly require organizations to demonstrate compliance and those who cannot document their choices and trade-offs are at great risk.
On the flip side, international data transfers have persisted as an important risk following landmark CJEU rulings on Schrems I (2015) and Schrems II (2020) which struck down the EU-US Safe Harbor and Privacy Shield. The EU-US Data Privacy Framework (2023) is now in place, but the legal situation of third-country transfers is politically sensitive and organizations must be prepared for the legal basis to be pulled away.
Finally, it is worth remembering that the GDPR was written before generative AI took off. Therefore, the rules on automated decision-making (GDPR, Art. 22) and data minimization are now supplemented/challenged by LLMs and AI systems, especially given the technical complexity and “black box” issues that AI inherently brings.”
The “Brussels Effect” often describes the influence that EU rules can have in defining global standards or inspiring similar legislation across the world. In your view, has GDPR become the norm outside the EU?
“Yes, absolutely! Globally, 144 countries now have some form of data protection legislation – a dramatic shift compared to 2018. Some countries’ frameworks have been directly inspired by GDPR, including Brazil’s LGPD (2020), India’s DPDPA (2023), and China’s PIPL (2021).
Furthermore, multinational companies on the EU market often use GDPR as a global standard for practical reasons – it is easier to have a high baseline than to adapt on a country-by-country basis.”
GDPR implementation has often been described as complex and challenging by supervisors and companies alike. Are there GDPR areas that companies find particularly challenging to comply with or are still misunderstood – and areas that are (surprisingly) well-implemented?
“The mentioned third-country transfers remain an ongoing challenge, particularly in light of recent developments affecting the implementation of the EU-US Data Privacy Framework, which in turn raises questions on the validity of the adequacy decision.
On a more granular level, Data Subject Access Requests (DSARs) can be challenging – it is surprisingly difficult, and sometimes time consuming, to comply with DSARs unless the necessary processes are built-in in systems that you use.
Among the areas that work well, the privacy-by-design approach in new systems is noteworthy, meaning newly developed products and services already include data protection.
“It is surprisingly difficult, and sometimes time-consuming, to comply with DSARs unless the necessary processes are built-in in the systems that you use.”
Fredrik Gustafsson
Another area is employee awareness and trainings. In the early days of GDPR, there were a couple of high-profile scandals where employees would introduce camera surveillance, tracking systems, or tracking pixels without the employer’s awareness. Today, employees generally understand the importance of data protection.”
Have there been any specific challenges that Sweden had to face?
“Sweden has had a system where businesses with government-issued publishing certificates are exempted from GDPR (constitutionally protected freedom of expression has triumphed over GDPR). The system was originally designed to protect newspapers and journalists ensuring that EU privacy rules would not interfere with free speech.
The option, however, has been open to a broad range of companies, resulting in a side-effect: online databases where Swedish citizens’ personal data, including criminal convictions, could easily be obtained for a fee.
The system was recently tested. On July 9, 2026, CJEU ruled against Lexbase, where it found that GDPR exemptions cannot be introduced for other than journalistic, academic, artistic, or literary purposes. The ruling’s impact is yet to be seen but online databases that include criminal convictions seem to be at risk.”
You have a long experience in carrying out data protection impact assessments (DPIA) for companies on the Swedish/Nordic market, with the latest assessments extending to AI. What are the main lessons from these processes?
“Under GDPR Art. 35, DPIAs need to be conducted before undertaking data processing that is “likely to result in high risk” to the rights and freedoms of individuals – and AI systems almost always trigger this given they easily fulfil the mandatory DPIA criteria (profiling, large-scale processing of personal data, new technologies).
Interestingly, the DPIA methodology assumes that risks can be identified and assessed before processing begins, but AI model behavior is often difficult to fully predict, including due to so-called “black box” issues.”
“Having worked on many DPIAs, the practical lessons I would highlight are:
- Treat the DPIA as a “living document” and an iterative process, not a one-time exercise.
- Make sure that cross-functional teams are aware and involved early on.
- Ensure that there is a documented process that covers changes to the data processing that might involve a high risk.
- Document trade-offs transparently: “We chose X over Y for the following reasons” – this is what supervisory authorities want to see.
- Be prepared that supervisory authorities will review DPIAs retrospectively.”
GDPR is facing simplification through the Digital Omnibus. If you had the possibility to “keep, toss, and expand” on elements from the GDPR considering their impact on personal data protection, what would you choose?
(keep = preserve from the current GDPR, toss = eliminate from the current GDPR, expand = add more detail/clarify/simplify)
“I find most parts of the GDPR sensible and motivated; it is rather the lack of clarity and implementation costs that can be challenged. I would keep the:
- Core principles (Art. 5) – Purpose limitation, data minimization, and storage limitation form the data protection foundations.
- Data subject rights (Art. 15–22) – Rights of access, rectification, erasure, and data portability are fundamental for individual personal data control.
- DPIA requirements for high-risk processing (Art. 35) – Particularly relevant for AI systems where risks may be difficult to foresee.
I would toss (or significantly simplify):
- Parts of the information requirements (Art. 13–14) – Lengthy, legally complex privacy policies are rarely read. Focus should be on clarity rather than comprehensiveness.
- (Although not part of the GDPR per se – but based on ECJ’s rulings) – Give the DPAs more flexibility to handle complaints in a more effective manner.
Finally, I would expand (add more detail/clarify):
- Harmonization of supervisory authority practices – Differences in application between Member States create uncertainty for organizations operating crossborder.”
The GDPR does not operate in isolation but interacts with the AI Act, DORA, DMA/DSA. How do you see this interaction?
“GDPR remains the horizontal “constitution” for personal data protection – it is technology-neutral and always applies alongside sector-specific regulation. DMA, DSA, and the AI Act add requirements on top of GDPR. Any system processing personal data must comply with both GDPR and the applicable sectoral act.
“AI systems almost always trigger Data Protection Impact Assessments (DPIA) under GDPR, Art.35.”
Fredrik Gustafsson
“The EU’s AI Act brings a risk-based approach to AI, with prohibitions on certain AI applications and strict requirements for high-risk systems. The demarcation against GDPR is central: AI Act regulates the system, GDPR regulates personal data processing – both apply in parallel and have an interesting interplay such as in automated decision-making.
Another concrete touchpoint can be the conformity assessments under the AI Act, which overlap with DPIA under GDPR and to some extent with DORA. Companies should try to set up coordinated processes to avoid duplication of work.”
What should be the top-of-mind considerations for companies and regulators as they navigate a changed data protection landscape today?
“My main recommendations for companies would include:
- Integrate data protection in AI governance and information security – not as an isolated compliance function and using a risk-based approach.
- Set up and see the value of having cross-functional teams.
- Monitor developments regarding US data transfers – the EU-US Data Privacy Framework may be challenged, and transfers could become restricted.
As for regulators, I think the priority should be in ensuring better coordination between parallel regulatory frameworks (GDPR, AI Act, Data Act, NIS2, DORA).”
Looking ahead, what does the near future of data protection look like?
“I think we will see AI regulation maturity, with better-defined interplay between the AI Act and the GDPR, but also perhaps a GDPR evaluation and possible review.
Regulatory fragmentation will remain a challenge, despite the harmonization ambitions. At the same time, there is an opportunity to use data protection as a competitive advantage – companies that take privacy seriously build greater customer loyalty.”
What are you looking forward to this autumn/by the end of 2026?
“I will remain focused on advisory services at the intersection of data protection, AI, and cybersecurity. In the next period, I look forward to the launch of our own AI Agents, with the first one being a Data Protection Agreement Assessment Tool.”